Network-Security
Question 1 |
The value of 351 mod 5 is ______.
3 | |
5 | |
2 | |
1 |
⇒ 31 = 3 ⇒ 3 mod 5 = 3
32 ⇒ 9 mod 5 = 4
33 ⇒ 27 mod 5 = 2
34 ⇒ 81 mod 5 = 1
35 ⇒ 243 mod 5 = 3
For every four numbers sequence is repeating.
So, (51 % 4) = 3
⇒ 33 = 27
⇒ 27 mod 5 = 2
Question 2 |
2N | |
N(N – 1) | |
N(N – 1)/2 | |
(N – 1)2 |
(N 2) = N(N – 1)/2
The number of keys required in the system as a whole to satisfy the confidentiality requirement is:
N(N – 1)/2
Question 3 |
In an RSA cryptosystem, the value of the public modulus parameter n is 3007. If it is also known that Φ(n) = 2880, where Φ() denotes Euler's Quotient Function, then the prime factor of n which is greater than 50 is ______.
107 | |
97 | |
45 | |
92 |
n = 3007, fi(n) = 2880 → fi(n) = (p – 1) (q – 1),
where p, q are prime factor of n.
The unit place of n is 7, it is a prime number and factor will be
1.7=7
11*17
21*37
31*47
….
31*97 =>3007
n = 3007 => 31*97
Therefore, 31 & 97 are the two prime numbers, which is satisfying the condition and 97 is greater than 50.
So, 97 is the correct answer.
Other methods:
When ϕ(n) is given when n=pq where p and q are prime numbers, then we have
ϕ(n) = (p−1)(q−1) = pq−(p+q)+1
But pq=n,
therefore, ϕ(n) = n−(p+q)+1 and p+q = n+1−ϕ(n).
Now, p and q are the roots of the equation,
x2 − (p+q)x + pq = (x-p)(x-q)
Substituting for p+q and pq in the above equation
x2 - (n+1-ϕ(n))x + n
Question 4 |
Using public key cryptography, X adds a digital signature to message M, encrypts <M, σ>, and sends it to Y, where it is decrypted. Which one of the following sequences of keys is used for the operations?
Encryption: X’s private key followed by Y’s private key; Decryption: X’s public key followed by Y’s public key | |
Encryption: X’s private key followed by Y’s public key; Decryption: X’s public key followed by Y’s private key | |
Encryption: X’s public key followed by Y’s private key; Decryption: Y’s public key followed by X’s private key | |
Encryption: X’s private key followed by Y’s public key; Decryption: Y’s private key followed by X’s public key |
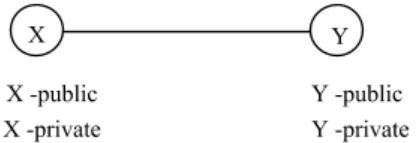
Encryption: Source has to encrypt with its private key for forming Digital signature for Authentication. Source has to encrypt the (M, σ) with Y’s public key to send it confidentially.
Decryption: Destination Y has to decrypt first with its private key, then decrypt using source public key.
Question 5 |
A layer-4 firewall (a device that can look at all protocol headers up to the transport layer) CANNOT
block entire HTTP traffic during 9:00PM and 5:00AM | |
block all ICMP traffic | |
stop incoming traffic from a specific IP address but allow outgoing traffic to the same IP address | |
block TCP traffic from a specific user on a multi-user system during 9:00PM and 5:00AM |
(B) Possible because it is network layer protocol.
(C) Possible because SP address is present in Network layer.
(D) Not possible, because to block specific user, we need user id which is present in Application layer.
Question 6 |
The total number of keys required for a set of n individuals to be able to communicate with each other using secret key and public key crypto-systems, respectively are:
n(n-1) and 2n | |
2n and n(n-1)/2 | |
n(n-1)/2 and 2n | |
n(n-1)/2 and n |
nC2 = n(n-1)/2
In case of public key, each sender has its own public key as well as private key. So, no. of keys are 2n.
Question 7 |
Consider the following two statements:
(i) A hash function (these are often used for computing digital signatures) is an injective function.
(ii) An encryption technique such as DES performs a permutation on the elements of its input alphabet.
Which one of the following options is valid for the above two statements?
Both are false | |
Statement (i) is true and the other is false | |
Statement (ii) is true and the other is false | |
Both are true |
ii) It uses the P-Box permutation.
Statement-I is false, II is true.
Question 8 |
Your are given the following four bytes :
10100011 00110111 11101001 10101011Which of the following are substrings of the base 64 encoding of the above four bytes?
zdp | |
fpq | |
qwA | |
oze |
10100011 00110111 11101001 10101011
So, in total we have 32 bits. And for base 64 we need 6 digits of binary no. to represent one digit of base 64 no.
So lets padd 4 bits on RHS, so that total digits will become 36 and we can separate then as group of 6 digits each.

Now, the longest substring will be from checking option is 'fpq'.
Question 9 |
In the RSA public key cryptosystem, the private and public keys are (e, n) and (d, n) respectively, where n = p*q and p and q are large primes. Besides, n is public and p and q are private. Let M be an integer such that 0 < M < n and f(n) = (p- 1)(q-1). Now consider the following equations.
I.   M’= Me mod n
     M = (M’)d mod n
II.  ed ≡ 1 mod n
III. ed ≡ 1 mod f(n)
IV.  M’= Me mod f(n)
     M = (M’)d mod f(n)
Which of the above equations correctly represent RSA cryptosystem?
I and II | |
I and III | |
II and IV | |
III and IV |
1. Generate randomly two “large” primes p and q.
2. Compute n=pq and ∅=(p-1)(q-1).
3. Choose a number e so that
gcd(e,∅)=1
4. Find the multiplicative inverse of e modulo ∅, i.e., find d so that
ed≡1 (mod ∅)
This can be done efficiently using Euclid’s Extended Algorithm.
The encryption public key is KE=(n,e) and the decryption private key is KD=(n,d).
The encryption function is
E(M)=Me mod n
The decryption function is
D(M)=Md mod n
Question 10 |
Which of the following statement(s) is TRUE?
1. A hash function takes a message of arbitrary length and generates a fixed length code.
2. A hash function takes a message of fixed length and generates a code of variable length.
3. A hash function may give the same hash value for distinct messages.
1 only | |
2 and 3 only | |
1 and 3 only | |
2 only |
(2) Statement-2 is wrong, refer statement-1.
(3) Statement-3 is correct, for example hash function N%10, this will generate same values for 1 as well as 2!
Question 11 |
A sender is employing public key cryptography to send a secret message to a receiver. Which one of the following statements is TRUE?
Sender encrypts using receiver’s public key | |
Sender encrypts using his own public key | |
Receiver decrypts using sender’s public key | |
Receiver decrypts using his own public key |
Question 12 |
WMEKREETSILTWETCOOCYONRU! | |
EETSICOOCYWMEKRONRU!LTWET | |
LTWETONRU!WMEKRCOOCYEETSI | |
ONRU!COOCYLTWETEETSIWMEKR |
Question 13 |
Is desirable property of the cryptographic algorithm | |
Is undesirable property of the cryptographic algorithm | |
Has no effect on the encryption algorithm | |
None of the above |
→ In the case of high-quality block cyphers, such a small change in either the key or the plaintext should cause a drastic change in the ciphertext.
Question 14 |
You can control where traffic goes in the three networks | |
You can do stateful packet filtering | |
You can do load balancing | |
Improve network performance |
1. The first firewall (also called the "front-end" or "perimeter" firewall) must be configured to allow traffic destined to the DMZ only.
2. The second firewall (also called "back-end" or "internal" firewall) only allows traffic from the DMZ to the internal network.
This setup is considered more secure since two devices would need to be compromised. There is even more protection if the two firewalls are provided by two different vendors because it makes it less likely that both devices suffer from the same security vulnerabilities.
Question 15 |
RSA Algorithm | |
Diffie-Hellman Algorithm | |
Electronic Code Book Algorithm | |
None of the above |
Question 16 |
Mutual authentication of client & server | |
Secret communication | |
Data Integrity protection | |
Error detection and correction |
It is utilized to encrypt Web traffic using Hypertext Transfer Protocol (HTTP) and to authenticate Web servers, and to encrypt communications between Web browsers and Web servers etc.
So, other than error detection and correction, all options are correct.
Question 17 |
X.25 | |
X.301 | |
X.409 | |
X.509 |
Question 18 |
his public key | |
his private key | |
receiver’s public key | |
receiver’s private key |
Question 19 |
64 bits | |
128 bits | |
512 bits | |
1024 bits |
→ It can still be used as a checksum to verify data integrity, but only against unintentional corruption. It remains suitable for other non-cryptographic purposes, for example for determining the partition for a particular key in a partitioned database.
Question 20 |
Browser security | |
FTP security | |
Email security | |
None of the above |
→ It uses Digital Signatures to provide authentication and integrity checking basically to check if the message is actually sent by the person or entity claimed to be the sender.
Question 21 |
Decrypt the message “WTAAD” using the Caesar Cipher with key = 15.
LIPPS
| |
HELLO
| |
OLLEH | |
DAATW |

We decrypt one character at a time. Each character is shifted 15 characters up Letter W is decrypted to H shifted 15 characters up. Letter W is decrypted to H. Letter T is decrypted to E. The first A is decrypted to L. The second A is decrypted to L And finally D is The second A is decrypted to L. And, finally, D is decrypted to O. The plain text is HELLO.
Question 22 |
Encrypt the Message “HELLO MY DEARZ” using Transposition Cipher with

HLLEO YM AEDRZ | |
EHOLL ZYM RAED | |
ELHL MDOY AZER | |
ELHL DOMY ZAER |
Here, key size = 4. So, character block size is 4.
Step-2: Remove the spaces in the message and write into sequential order.

Step-3: Get cipher text according to ascending order is ELHL MDOY AZER.
Question 23 |
Layer 2 firewall | |
Layer 3 firewall | |
Layer 4 firewall | |
Layer 7 firewall |
→ A transparent firewall, on the other hand, is a Layer 2 firewall that acts like a "bump in the wire," or a "stealth firewall," and is not seen as a router hop to connected devices.
Question 24 |
Encryption : X’s private key followed by Y’s private key. Decryption : X’s public key followed by Y’s public key. | |
Encryption : X’s private key followed by Y’s public key; Decryption : X’s public key followed by Y’s private key | |
Encryption : X’s private key followed by Y’s public key; Decryption : Y’s private key followed by X’s public key. | |
Encryption : X’s public key followed by Y’s private key; Decryption : Y’s public key followed by X’s private key. |
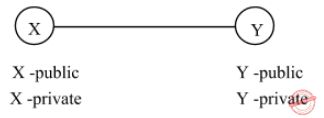
Encryption: Source has to encrypt with its private key for forming Digital signature for Authentication. Source has to encrypt the (M, σ) with Y’s public key to send it confidentially. Decryption: Destination Y has to decrypt first with its private key, then decrypt using source public key.
Question 25 |
IP packet with same header
| |
IP packet with new header
| |
IP packet without header
| |
No changes in IP packet |
IPSec Tunnel mode: In IPSec Tunnel mode, the original IP packet (IP header and the Data payload) is encapsulated within another packet.
In IPSec tunnel mode the original IP Datagram from is encapsulated with an AH (provides no confidentiality by encryption) or ESP (provides encryption) header and an additional IP header. The IP addresses of the newly added outer IP header are that of the VPN Gateways.
The traffic between the two VPN Gateways appears to be from the two gateways (in a new IP datagram), with the original IP datagram is encrypted (in case of ESP) inside IPSec packet.
Question 26 |
3 | |
7 | |
27 | |
40 |
1. Choose two distinct prime numbers p and q.
2. Compute n = pq.
3. Compute λ(n) = lcm(λ(p), λ(q)) = lcm(p − 1, q − 1), where λ is Carmichael's totient function. Choose an integer e such that 1 < e < λ(n) and gcd(e, λ(n)) = 1; i.e., e and λ(n) are coprime.
4. Determine d as d ≡ e−1 (mod λ(n)); i.e., d is the modular multiplicative inverse of e modulo λ(n). This means: solve for d the equation d⋅e ≡ 1 (mod λ(n)).
Given two prime numbers are p = 5 and q = 11, encryption key, e = 27
n = p * q = 5 * 11 = 55
λ(n)= (p-1) * (q-1) = 4 * 10 = 40
Let the value of decryption key be ‘d’ such that:
e * d mod λ(n) = 1
27 * d mod 40 = 1
d = 3